Munish Kharb
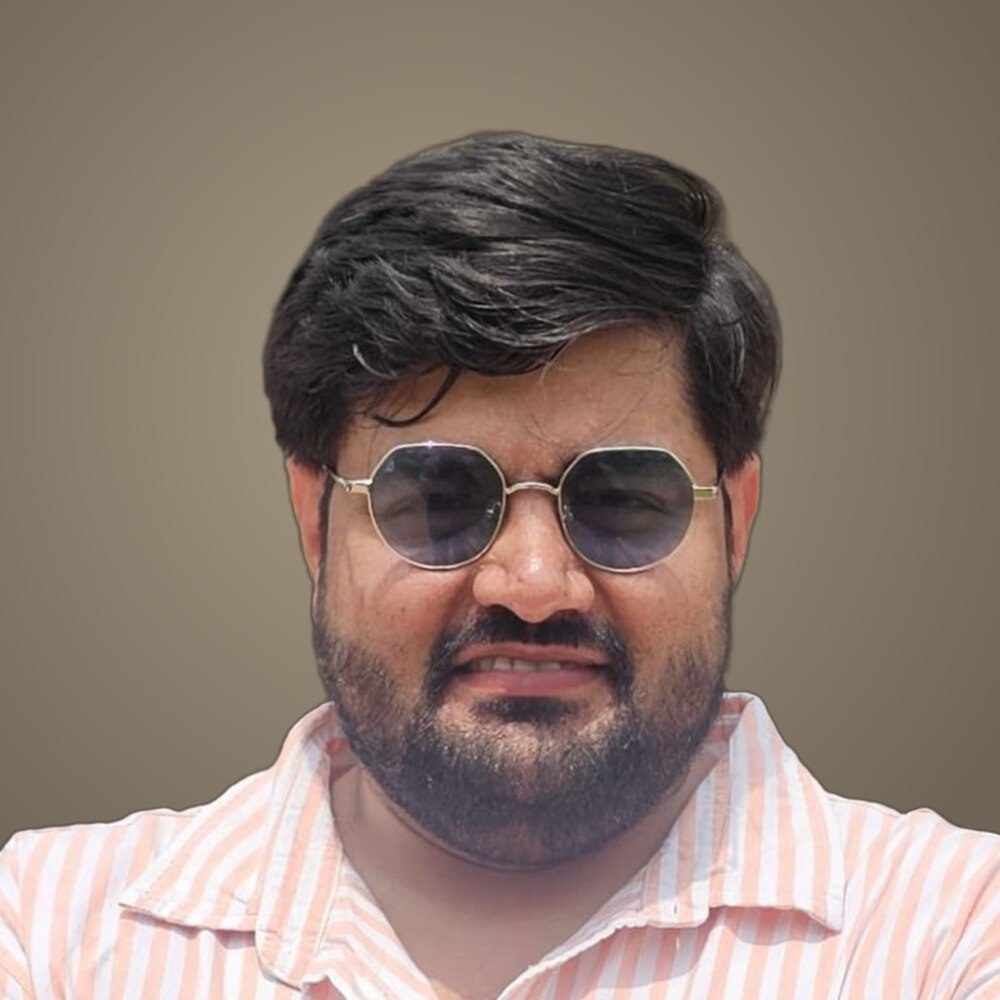
I'm a product security engineer working across application and cloud security. For seven years I have made products harder to break, from the design review before any code exists to the AWS account the code runs in.
Across healthtech, edtech, ePharmacy and gaming I have owned application and cloud security, run the whole security function, and led and mentored the team around it. I have stayed an engineer first, building the controls and writing the policies and audit evidence that go with them. How I think about the work is on my approach page.
It started in college with a glossy black Sony Vaio. It shipped with Windows; I put Linux on it, spent a year trying every distribution I could find, and landed on BackTrack, the tool that later became Kali Linux, reading about wireless security. My first job was web development with security at an edtech company, and within months I knew which half I stayed late for.
Right now I'm exploring how AI can change security processes and tooling, and building the tools below to test those ideas.
Experience
- Jun 2026 – Sep 2026Junglee GamesLead Security EngineerApplication and cloud security for two gaming products, from threat models to the secure-SDLC gate. The role ended when Junglee wound up operations after India's 2026 real-money gaming ban.
- Jan 2023 – Jun 2026Connect and HealSenior, then Lead Security EngineerBuilt and led the security function for a healthtech group of three entities, and mentored the team.
- Aug 2021 – Jan 2023PharmEasySecurity EngineerPentests and secure design reviews across PharmEasy, Retailio, Docon and Thyrocare.
- Mar 2020 – Aug 2021AcadbeeSecurity EngineerWeb application pentests, and Django applications built alongside the security work.
The resume has the full record.
Toolkit
Application security
Threat modeling (STRIDE, data-flow) · secure design and secure code review (Java, Python, JavaScript) · web, API, desktop and WebSocket pentesting · OAuth, JWT and SAML · business-logic, payment-flow and multi-tenant authorization testing
- Burp Suite Pro & Enterprise
- Caido
- OWASP ZAP
- Nuclei
- httpx
- ProjectDiscovery suite
- Amass
- Shodan
- Postman
- sqlmap
- ffuf
- Nmap
- Wireshark
- Qualys
- DefectDojo
Mobile and reverse engineering
Mobile pentesting (MASVS/MASTG) on Android and iOS · reverse engineering and dynamic instrumentation · Flutter and Unity apps
- Frida
- Objection
- MobSF
- Jadx
- Apktool
- Drozer
- Ghidra
- radare2
- Il2CppDumper
- reFlutter
- Blutter
- Hopper
- Charles Proxy
Cloud and infrastructure (AWS)
Multi-account posture and hardening · IAM, KMS, VPC · EKS and Kubernetes · CloudTrail, GuardDuty, Security Hub · WAF · CSPM and CNAPP · IaC security · CI/CD-to-cloud threat modeling
- AWS Organizations
- IAM
- KMS
- CloudTrail
- GuardDuty
- Security Hub
- Wiz
- OX Security
- Prowler
- ScoutSuite
- Pacu
- CloudFox
- Checkov
- tfsec
- Trivy
- Terraform
- kube-bench
- Plerion
- Sysdig
- Sweet Security
- SentinelOne CNAPP
Detection and monitoring
SIEM operation on Wazuh · MITRE ATT&CK-mapped rules · Sigma and YARA tuning · CloudTrail detections · alert tuning and suppression · detection-as-code via GitOps
- Wazuh
- OpenSearch
- ELK
- osquery
- Sysmon
- auditd
- Suricata
- YARA
- ClamAV
- Sigma / pySigma
- Stratus Red Team
- OpenCTI
- VirusTotal
- Coralogix
- Velociraptor
AI and LLM security
LLM and chatbot pentesting (prompt injection, data and tool/API reach, session binding) · AI agent and MCP security: least privilege, tool-reach review, isolation, human-gated actions · RAG and agent threat modeling · secure read-only agent access to infrastructure · AI usage governance and policy
- Prompt-injection and jailbreak testing
- agent least-privilege and tool-reach review
- read-only MCP design
- OWASP LLM Top 10
- MITRE ATLAS
- AI-assisted analysis
DevSecOps and supply chain
CI/CD security gates (SAST, DAST, SCA, secrets) · SBOM and CVE correlation · ASPM program design, severity and SLA · branch protection · GitOps · phased developer rollout · Python, Java, JavaScript, Bash
- Semgrep / OpenGrep
- TruffleHog
- Gitleaks
- Syft
- Grype
- CycloneDX
- Dependency-Track
- OWASP Dependency-Check
- pre-commit
- SonarQube
- Checkov
- Bitbucket Pipelines
- GitHub Actions
- Jenkins
- Argo CD
Governance and corporate security
ISO 27001 and 27701 · SOC 2 Type 2 · NIST CSF and SSDF · GDPR and DPDP · security policy through audit evidence · vendor and customer security assessments · access reviews · awareness and phishing programs · endpoint, DLP, MDM and email security
- Scrut
- SentinelOne EDR
- Endpoint Protector DLP
- Scalefusion
- JumpCloud
- Fortinet
- Sophos
- Google Workspace admin
Reading
On the desk now, and a few from off the clock: Indian history, international relations, and lately Murakami.
- The CloudSec EngineerMarco Lancini · reading now
- JavaScript for HackersGareth Heyes · reading now
- Alice and Bob Learn Application SecurityTanya Janca
- The City and Its Uncertain WallsHaruki Murakami · reading now
- India After GandhiRamachandra Guha
The rest of the shelf, Hindi and Urdu poetry included, is on the reading page.
Last updated 2 Oct 2026